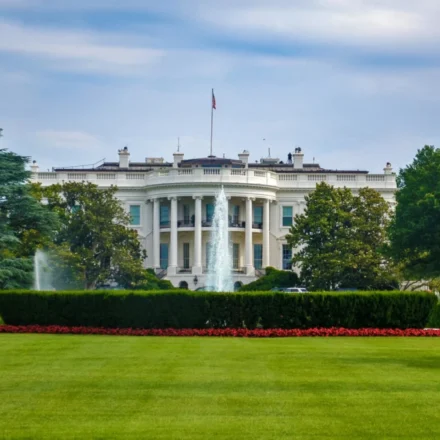
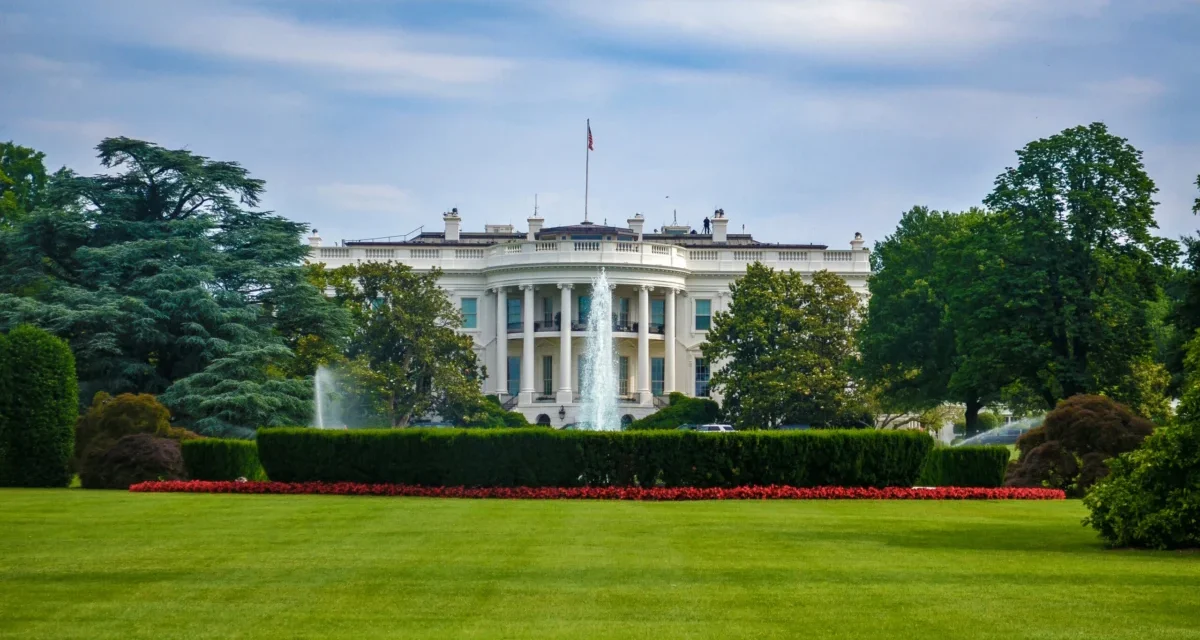




In a startling revelation that underscores the fragility of modern network security, cybersecurity researchers have identified signs of residential proxy software operating from within the Executive Office of the President of the United States. The discovery, facilitated by the Residential Proxy Observatory, suggests that a device connected to the White House network—a high-security perimeter—is being utilized as an exit node for a residential proxy network. This development raises profound questions regarding the integrity of federal digital infrastructure and the increasingly pervasive nature of obfuscation technologies in the modern internet ecosystem.
The Nature of the Breach: What are Residential Proxies?
To understand the gravity of this discovery, one must first understand the mechanism of a residential proxy. Unlike traditional data center proxies, which originate from known server farms, residential proxies reroute internet traffic through IP addresses assigned to residential internet service providers (ISPs) and their associated hardware.
By piggybacking on a legitimate home or office device, malicious actors can mask their true identity and location. When an entity engages in a cyberattack—such as a Distributed Denial of Service (DDoS) strike, credential stuffing, or large-scale phishing—the traffic appears to originate from a standard, trusted user rather than a suspicious server.
When this technology is deployed within an enterprise or government network, the implications are doubled: not only is the network being used to facilitate external malicious activity, but a device within that network has likely been compromised by third-party software, potentially creating a "backdoor" into a high-value environment.
Chronology of the Discovery
The identification of this anomaly was the result of ongoing monitoring by the Residential Proxy Observatory, a project spearheaded by Layer3 Intel. The observatory tracks "proxy exit activity" by scanning the global internet for nodes that exhibit the behavioral patterns of residential proxy networks.
The Initial Flag
In recent weeks, researchers identified a persistent stream of traffic originating from AS2650. This autonomous system is explicitly registered to the Executive Office of the US President. The traffic patterns observed were consistent with residential proxy nodes—specifically, the device was actively relaying traffic for external users, effectively turning a White House-authorized device into a relay point for potentially illicit internet activity.
Validation and Cross-Referencing
Upon flagging the activity, Layer3 Intel analysts conducted rigorous cross-referencing to ensure that the detected traffic was not a result of authorized government testing or legitimate, sanctioned VPN activity. The behavioral signature of the detected software—characterized by high-volume, randomized request patterns—mirrored the telemetry seen in known commercial residential proxy networks, rather than the stable, encrypted tunnels typical of secure government communications.
Broadening the Scope
The finding is not an isolated incident. The Residential Proxy Observatory has tracked similar nodes across diverse and unexpected geographies, including the remote island of St. Helena. This demonstrates that the proxy network ecosystem is not confined to urban centers or high-tech hubs; it is a global, distributed, and essentially invisible mesh network that operates beneath the radar of traditional perimeter security.
Supporting Data: A Global Problem
The incident at the White House is merely the latest, albeit most high-profile, data point in a growing body of research. A comprehensive report from Infoblox earlier this year highlighted that residential proxies are "hiding in plain sight" within major enterprise networks.
The Scale of Proliferation
According to the research, residential proxy providers often recruit devices via "freemium" software—such as free VPN apps, browser extensions, or "reward-based" applications. Users unknowingly install this software, granting it permission to utilize their idle bandwidth. Once installed, the device is enrolled in a proxy pool. The owner of the device remains largely unaware that their IP address is being sold to third parties, who may use it for anything from ad-fraud and web scraping to illegal hacking operations.
Data Patterns
The Residential Proxy Observatory utilizes a combination of active scanning and passive traffic monitoring to build a real-time heat map of these nodes. The data suggests that:
- Infiltration Rate: A significant percentage of corporate and government-registered IPs show evidence of residential proxy traffic.
- Persistence: Once a device is infected with a proxy agent, it often remains active for weeks or months, as standard antivirus software frequently categorizes these applications as "potentially unwanted programs" (PUPs) rather than high-risk malware.
- The "Exit" Factor: By design, these proxies are intended to facilitate egress traffic. This makes them a preferred tool for threat actors who need to bypass IP-based reputation filters.
Official Responses and Security Posture
As of this writing, official comment from the White House regarding the specific device identified has been limited. However, cybersecurity experts emphasize that the presence of such software is an indictment of modern "Bring Your Own Device" (BYOD) policies and the lack of robust egress filtering on government networks.
Government agencies are governed by strict Zero Trust architectures. The presence of a residential proxy suggests a failure in the "Verify Explicitly" pillar of Zero Trust, as the device was presumably permitted to authenticate with the network despite running non-approved, unauthorized software.
Security analysts have suggested that the White House IT security teams are likely conducting a "scrub" of all network-connected devices to identify the specific hardware involved. The goal will be to determine how the software was introduced—whether through an employee’s unauthorized browser extension, a compromised IoT device (such as a smart printer or thermostat), or a more sophisticated vector of attack.
The Implications: Why This Matters
The discovery of a residential proxy within the White House network carries grave implications for national security, legal liability, and digital ethics.
1. National Security and Attribution
If an attack on a foreign state or a private corporation is traced back to a White House IP address, it complicates the United States’ ability to maintain its posture on international cybersecurity norms. Attribution becomes a geopolitical minefield; the US government could be wrongly accused of state-sponsored cyber warfare, or conversely, it may find itself unable to identify the actual threat actor utilizing the relay.
2. Legal and Regulatory Liability
Residential proxy providers often operate in a legal gray area. While the software itself is not inherently "illegal," its function is to obfuscate the origin of digital activity. If a government network is being used to facilitate illegal acts—such as the distribution of child exploitation material, malware, or stolen credentials—the network owner could potentially face legal hurdles or be flagged by international cybersecurity law enforcement agencies.
3. The Erosion of Perimeter Security
The "White House incident" proves that even the most secure network perimeters are permeable. If a residential proxy can establish a foothold in the most guarded network on Earth, it highlights the vulnerability of the entire global internet infrastructure. The reliance on "trusted" residential IPs has created a loophole that renders traditional IP-based security measures increasingly obsolete.
4. The Threat of Insider Knowledge
While it is likely that the proxy was installed inadvertently—perhaps by an employee installing a "free" tool for personal convenience—it is impossible to rule out intentional infiltration. The ability to exfiltrate data from a high-security network through an authorized, open channel (like a residential proxy exit node) is a "Holy Grail" for advanced persistent threats (APTs).
Conclusion: A Call for Vigilance
The infiltration of the White House network by residential proxy software serves as a definitive wake-up call for the cybersecurity community. It demonstrates that the threat is no longer just about external attackers breaching firewalls; it is about the "Trojan horse" applications that reside within our networks, granted permission by users who are unaware of the security trade-offs they are making.
Moving forward, organizations—from the White House down to private enterprises—must implement stricter control over software installations, enhance egress traffic monitoring, and foster greater awareness regarding the dangers of "free" internet tools. The era of the invisible proxy is here, and as the White House discovery proves, there is no longer a place on the planet—or in the network—where the impact of digital interference cannot reach.
The security of the digital future depends on our ability to distinguish between a legitimate user and a masked proxy, and until that distinction is made absolute, the integrity of our most sensitive networks remains at risk.